Examining Encryption Standards in Cross-Border Charge Processing for Subscription-Based Platforms
Ulrich Baumann · Aug 21, 2026
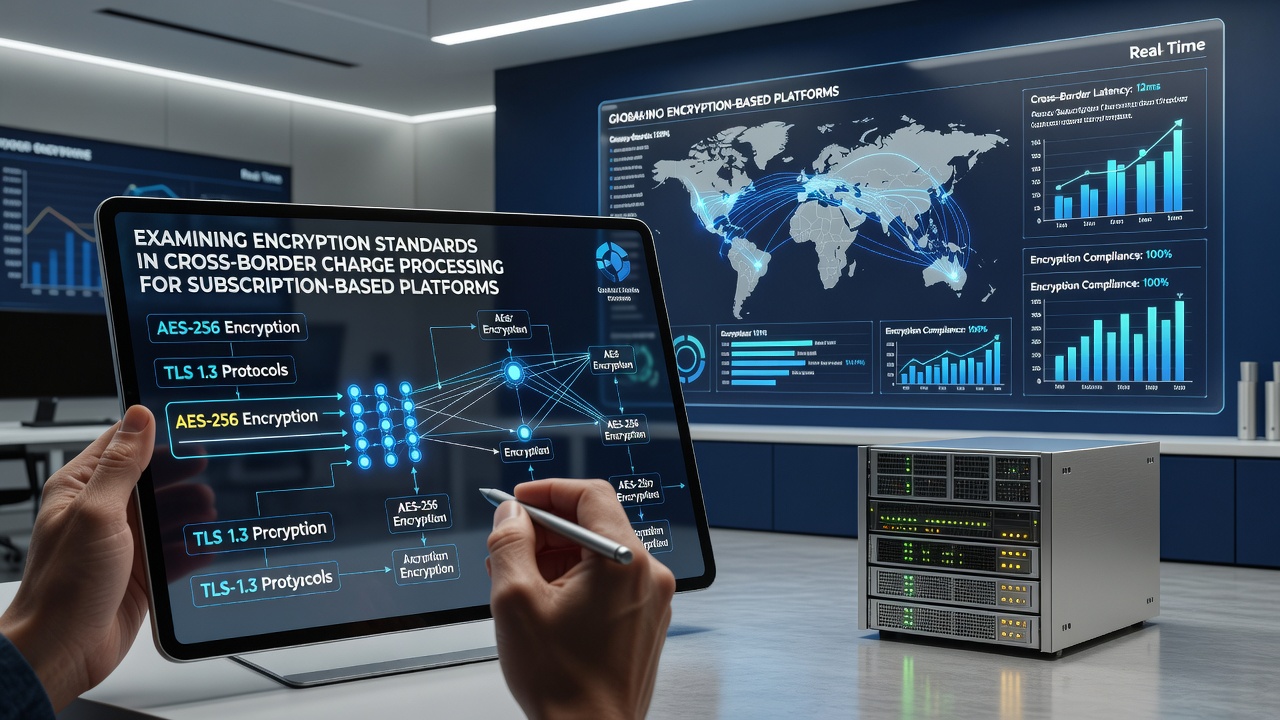
Examining Encryption Standards in Cross-Border Charge Processing for Subscription-Based Platforms
Encryption standards form the backbone of secure data transmission when subscription platforms handle recurring charges across national borders, and those standards continue to evolve as transaction volumes grow. Subscription models rely on consistent authorization flows that must protect cardholder data, personal identifiers, and billing details while complying with varying regulatory frameworks in each jurisdiction.
Core Encryption Protocols in Use
Transport Layer Security version 1.3 serves as the current baseline for protecting data in transit between merchant systems and payment processors, while Advanced Encryption Standard with 256-bit keys remains the preferred method for encrypting stored data at rest. Researchers at the National Institute of Standards and Technology have documented how these algorithms resist known attack vectors when implemented with proper key rotation schedules and certificate management practices.
Platforms processing international subscriptions often combine these protocols with application-level encryption so that sensitive fields remain protected even after initial decryption at the payment gateway. Data shows that organizations maintaining separate encryption layers reduce exposure during the brief windows when information moves between internal services.
Regional Regulatory Influences on Implementation
Cross-border operations must satisfy overlapping requirements from multiple authorities. The European Union Agency for Cybersecurity has published guidance that aligns with the Payment Services Directive requirements, whereas regulators in Singapore and Australia emphasize additional controls for data residency and key custody. Subscription providers therefore maintain region-specific encryption configurations that activate based on the location of each customer account.
As of August 2026, several jurisdictions introduced updated guidance requiring periodic audits of encryption implementations used in recurring billing environments. These audits focus on verifying that key lengths, cipher suites, and certificate lifespans meet the newest benchmarks without disrupting authorization success rates.
Operational Challenges in Multi-Jurisdiction Environments
Latency introduced by encryption and decryption steps can affect authorization timing, especially when charges cross multiple network hops between the subscriber, the platform, and the acquiring bank. Observers note that platforms mitigate this by deploying hardware security modules in regional data centers so that cryptographic operations occur closer to the point of authorization.
Key management presents another layer of complexity. When customer data originates in one country and gets processed in another, organizations must decide whether to replicate keys, use envelope encryption, or rely on cloud-based key management services that satisfy local sovereignty rules. Studies from academic institutions have examined how different key-distribution models perform under high-volume recurring transaction loads.
Integration with Existing Payment Infrastructure
Many subscription platforms connect to payment processors through APIs that already enforce TLS 1.3 and support field-level encryption for recurring payment tokens. This approach allows the platform to avoid storing full card numbers while still enabling seamless renewals. Industry reports indicate that adoption of these API-level protections has increased steadily as processors expand support for additional cipher suites and shorter certificate validity periods.
Testing environments replicate production encryption settings so that developers can verify that new features do not weaken cryptographic controls. Automated scans flag deprecated algorithms before code reaches live systems, reducing the window during which weaker standards might remain active.
Future Developments and Standardization Efforts
Work continues on post-quantum cryptographic algorithms that could eventually replace current public-key methods in payment flows. Standards bodies have begun publishing draft recommendations that organizations can evaluate without immediate production deployment. Subscription platforms with long development cycles have started pilot programs to assess performance impact on authorization latency and key-exchange overhead.
Collaboration between payment networks and regulatory agencies has produced reference architectures that combine encryption requirements with fraud-detection signals. These architectures allow platforms to share encrypted metadata that supports risk scoring while preserving confidentiality of individual transaction details.
Conclusion
Encryption standards in cross-border subscription charge processing continue to advance in response to regulatory updates, performance requirements, and emerging threats. Organizations that align their implementations with documented benchmarks from bodies such as the National Institute of Standards and Technology and the European Union Agency for Cybersecurity maintain stronger positions for handling recurring international payments. Ongoing monitoring of algorithm performance and key-management practices supports reliable authorization flows as transaction patterns shift.